Linux permissions decide which users can read, change or run a file, and which users can list or enter a directory. This guide walks through how to inspect permissions, change them safely and diagnose access problems. The current RHCSA EX200 exam is based on RHEL 10; always check Red Hat’s objectives for the version you are taking.
Quick reference: start with ls -l and stat, then check the path, owner, group and mode. Use getfacl for extra ACL rules and ls -Z when SELinux may be involved.
| Task | Command | What it tells you |
|---|---|---|
| Inspect mode and owner | ls -l file | Symbolic mode, owner and group |
| Read numeric mode | stat -c '%A %a %U:%G %n' file | Mode, octal value and ownership |
| Change permissions | chmod 640 file | Owner read/write; group read; others none |
| Set ownership | sudo chown user:group file | Assign an existing user and group |
| Check new-file defaults | umask | Show the current shell’s creation mask |
| Check extra access rules | getfacl file | Show POSIX ACL entries and effective limits |
How to find file and file system permissions
For hands-on practice, use a new empty directory. If this name already exists, choose another one so the examples stay separate from your files.
mkdir ~/permissions-lab
cd ~/permissions-lab
touch report.txt script.sh
mkdir projectLinux evaluates the owner, owning group and everyone else. Each class can have read (r), write (w) and execute (x) permissions. For a file, execute means the file can be run as a program. For a directory, read allows listing names, execute means search or traverse, and write allows creating or removing entries when combined with execute.
Stat command
Use stat to see a file’s mode and ownership in a consistent format. The numeric form is useful when you need to confirm a specific mode; the symbolic form makes it easier to read.
stat -c '%A %a %U:%G %n' report.txt
stat -c '%A %a %U:%G %n' project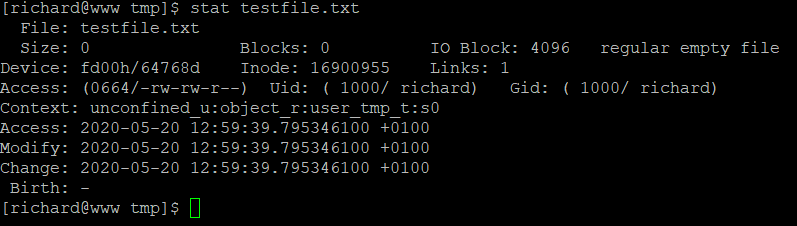
In the output, -rw-rw-r-- describes a regular file. The first character is the object type; the next three characters are the owner’s permissions, followed by the group’s and others’ permissions. A directory begins with d.
The LS command
Use ls -l for files and ls -ld when you want the directory’s own permissions rather than a listing of its contents. The mode is shown symbolically; it is not displayed in octal form.
ls -l report.txt
ls -ld project
ls -l project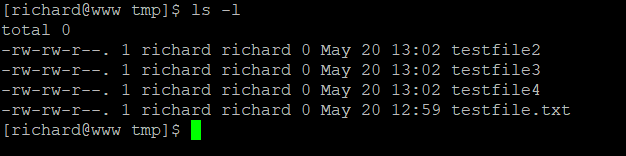
The trailing character can add useful context. A + indicates an extended access control list (ACL). On RHEL, a trailing . indicates a SELinux security context. In a mode such as drwxrwxrwt., the t is the sticky bit; the final period relates to SELinux.
Change permissions and ownership
Chmod
Use chmod to change the mode of an existing file or directory. The common octal values are 4 for read, 2 for write and 1 for execute. Add the values within each class: 7 is rwx, 5 is r-x and 0 grants no access.
chmod 754 script.sh
chmod u=rw,g=r,o= report.txt
chmod g+w report.txt
stat -c '%A %a %n' script.sh report.txt
chmod 754 script.sh gives the owner read, write and execute; the group read and execute; and others read. Symbolic modes can be easier for small changes: chmod g+w report.txt adds group write permission while preserving the other bits.
Be deliberate with directory permissions. Group members need both write and execute to create or remove entries; execute alone lets them traverse the directory. Avoid using chmod 777 as a general fix because it grants write access to every local user. The creation mask does not filter a later chmod operation.
Chown
Use chown to change a file’s owner, or its owner and group together. Use chgrp when only the group needs to change. These examples assume the account and group already exist; use getent group developers to check a group name.
sudo chown alice report.txt
sudo chown alice:developers report.txt
sudo chgrp developers report.txt
stat -c '%U:%G %A %a %n' report.txtChanging ownership usually requires root privileges. After the change, verify the result with stat or ls -l. A correct mode can still deny access when the file belongs to a different owner or group than expected.
Umask
The umask affects permissions when a process creates a new file or directory. It removes permissions from the base mode requested by the program. Regular files start from a base mode of 0666; directories start from 0777. The resulting mode also depends on the current umask, so inspect it instead of assuming every account has the same setting.
umask
(
  umask 027
  touch private.txt
  mkdir private-dir
  stat -c '%A %a %n' private.txt private-dir
)With a umask of 027, the example creates a regular file with mode 640 and a directory with mode 750. The subshell keeps the example’s umask change from affecting the surrounding terminal. A umask does not change existing files, and it does not add execute permission to newly created regular files.
A umask set at the prompt lasts for that shell and its child processes. Persistent defaults depend on the system’s login and shell configuration. Check the current RHEL documentation before changing a system-wide setting.
Set special permission bits
The first octal digit can set special bits. These are useful in specific cases and should be applied only when the intended access behaviour is understood.
Setuid and setgid
Setuid on an executable makes it run with the effective user ID of the file’s owner; setgid on an executable uses the file’s group. Both are security-sensitive. Avoid adding these bits to programs unless the application requires them and the consequences have been reviewed.
Setgid on a directory has a different, common use: files and subdirectories created inside inherit the directory’s group. Create a shared directory for a group that already has access, then set its group and mode:
sudo chgrp developers team
chmod 2770 team
stat -c '%A %a %U:%G %n' teamThe leading 2 sets setgid. New entries inherit the directory’s group, while their write permissions still depend on their creation mode and umask.
StickyBit
The sticky bit is mainly used on shared, writable directories. It limits who can remove or rename an entry: the file owner, directory owner or root. It does not grant write access by itself.
mkdir shared-drop
chmod 1770 shared-drop
stat -c '%A %a %n' shared-dropThe leading 1 sets the sticky bit. In ls -l, it appears as t in the others execute position when that execute bit is present; uppercase T appears when it is absent. The trailing period in an RHEL listing is a separate SELinux indicator.
Grant one user access with an ACL
Traditional permissions provide one owner and one group. A POSIX ACL can grant a named user or group access without changing the file’s owner. In this example, alice must exist and must be different from the file owner.
setfacl -m u:alice:r-- report.txt
getfacl report.txt
ls -l report.txtThe ACL mask limits the effective permissions of named users, named groups and the owning group. The group mode shown by ls -l reflects this mask when an extended ACL is present. A later chmod can change the mask and reduce an ACL entry’s effective access, so inspect the full result with getfacl.
Diagnose permission denied
Check each layer in order. A user needs search permission on every directory in the path; the final file’s mode alone does not explain every denial.
- Inspect each path component with
namei -l /path/to/report.txt. - Check the file’s mode, owner and group with
stat -c '%A %a %U:%G %n' /path/to/report.txt. - Check extended rules with
getfacl /path/to/report.txt. - On SELinux systems, inspect the label with
ls -lZ /path/to/report.txt. If the label is incorrect, restore the expected label withsudo restorecon -v /path/to/report.txt. - For a suspected SELinux denial, inspect recent audit events with
sudo ausearch -m AVC -ts recentwhen audit tools are installed.
Change only the layer that is wrong. Use chmod for discretionary mode bits, setfacl for an ACL, and SELinux tools for labels or policy. Avoid broad recursive permission changes while diagnosing a single path.
Practice task: protect a report and share a directory
Run this in a disposable account or test VM. It creates files under your home directory and keeps the temporary umask inside a subshell.
mkdir -p ~/permissions-lab/team
cd ~/permissions-lab
printf 'Internal report\n' > report.txt
chmod 640 report.txt
(
  umask 027
  touch private.txt
  mkdir private-dir
)
chmod 2770 team
stat -c '%A %a %U:%G %n' report.txt private.txt private-dir teamConfirm that report.txt is 640, private.txt is 640, private-dir is 750 and team is 2770. For a shared-group test, set team to an existing group with chgrp, then create a file inside it and check the inherited group with stat.
RHCSA mini-series
Continue with Grep and regular expressions, file management in Red Hat, or managing users and groups. The rest of the series covers root password recovery, using RHEL as a VM host, local storage and NTP configuration.
Leave a Reply